All in the Family: Evil Corp, Seven Years on the Wanted List
Seven years ago the US charged Evil Corp's alleged boss and put $5M on his head. He is still in Russia. A Timewarp on a family crime business with a line to the Russian state.
Hello there cyber fanatics!
Seven years ago, on December 5, 2019, the United States charged a 32-year-old from Moscow named Maksim Yakubets and offered up to $5 million for information leading to his arrest. He is still on the FBI's wanted list. As far as any public record shows, he has never been arrested, and he has never been convicted. And as far as anyone can tell, he is doing fine.
This is a Timewarp post, so let's go back and look at who these people are, because the people are the whole story here.
First, who is Evil Corp?
If you have never heard the name: Evil Corp is a cybercrime group based in Moscow. Yes, that is really what everyone calls them. The NCA says the name goes back to a web domain the group used in 2014.
Their first big product was Dridex. Dridex was banking malware, a program that hid inside an email attachment. You opened the "invoice", the malware installed itself quietly, waited for you to log in to your bank, and stole the login. The crew then used it to move money out of your account, usually through "money mules", people who receive the stolen money in their own bank accounts and pass it on.
Later the group moved to ransomware: malware that locks every computer in a company until the company pays.
The numbers, from the governments that chased them:
- More than $100 million stolen with Dridex, from around 300 banks and financial institutions in more than 40 countries (US Treasury, 2019).
- At least $300 million extorted with ransomware (UK National Crime Agency, the NCA, 2024).
Remember when?
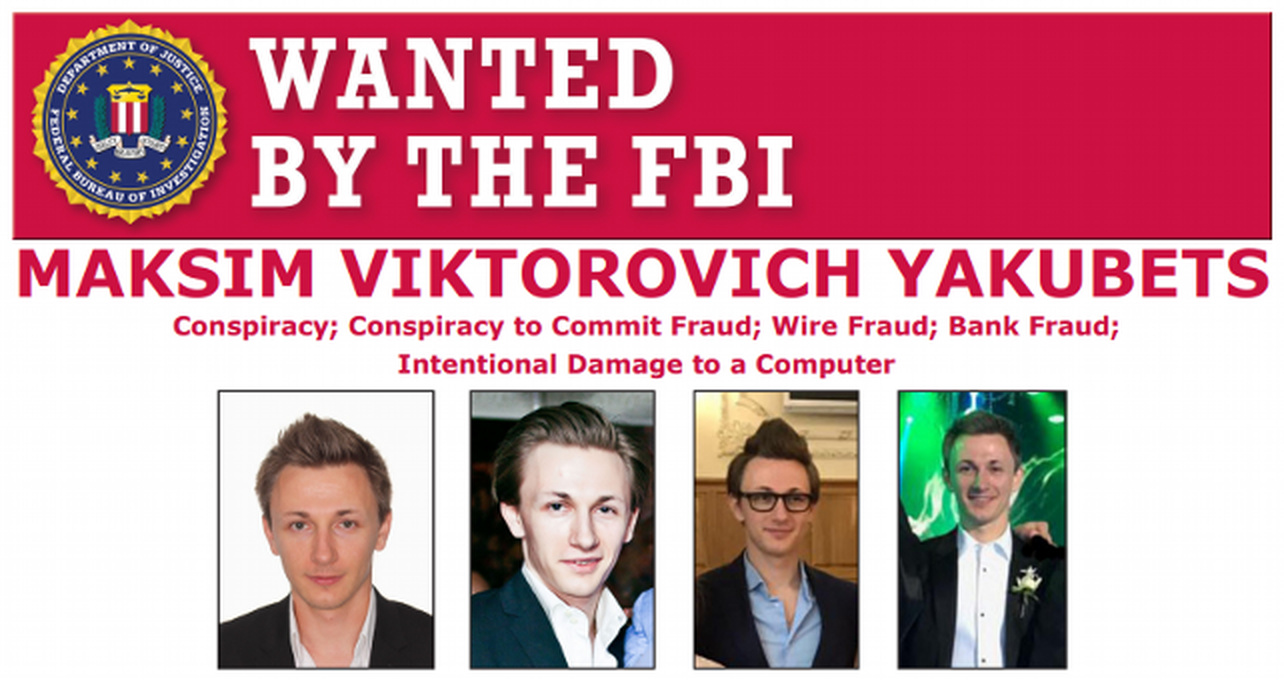
December 5, 2019 was a coordinated day. The US Department of Justice (DOJ) unsealed an indictment in Pittsburgh charging Yakubets and his administrator, Igor Turashev, with fraud, bank fraud and damaging computers. A second case in Nebraska tied Yakubets to the handle "aqua", from the old Zeus bank fraud case that goes back to 2009. Yes, that Zeus. If you were in this field around 2010 you remember it, and it is funny to see the same handle come back ten years later with a much nicer car.
The same day, the US Treasury's Office of Foreign Assets Control (OFAC), the office that runs US sanctions, sanctioned Evil Corp along with 17 individuals and 7 entities. And the State Department put up to $5 million on Yakubets. The FBI said at the time it was the largest reward ever offered for a cyber criminal.
Then the NCA released the part everyone remembers. Yakubets drove a custom Lamborghini with a personalised plate that reads "Thief" in Russian. He reportedly spent more than £250,000 on his wedding. Lynne Owens, then head of the NCA, said the Lamborghini "was someone's life savings, now emptied from their bank account."
The audacity of these people!
Meet the family
Most ransomware programs I have watched are built like startups. There is a core team, and around it there are affiliates, free agents who rent the ransomware, do the break-ins and take a cut. Affiliates go where the split is best. They come and go.
Evil Corp is a different model. In 2024 the NCA described it as "a family-centred operation based in Moscow, reminiscent of a traditional organised crime gang." According to the NCA:
- Maksim Yakubets, "aqua", is the boss.
- His father, his brother and two cousins were part of the group. The NCA says his father had past ties to money laundering, and the father was sanctioned by the US in 2024.
- His father-in-law, Eduard Benderskiy, is a former officer of the FSB, Russia's Federal Security Service. The US Treasury calls him "a key enabler of Evil Corp's relationship with the Russian state."
- His second-in-command, Aleksandr Ryzhenkov, was charged in the US in October 2024.
To be clear, the family members are sanctioned. They are not charged with any crime.
A day job at the FSB?
This is the part I find the most interesting, and it is also the part where I only know what the governments published.
The 2019 Treasury release said: "As of 2017, Yakubets was working for the Russian FSB." It also said that in April 2018 he was in the process of getting a license to work with Russian classified information from the FSB.
In 2024 the NCA went further. It said that before 2019, Russian intelligence tasked Evil Corp with cyber attacks and espionage against NATO allies, and that after the 2019 charges Benderskiy helped protect senior members, giving them security and shielding them from Russian internal authorities.
A senior Treasury official put it nicely back in 2019: it is "simply inconceivable" that the group could operate without the Russian government knowing.
So we have a group that steals money from banks, run by a family, with a former FSB officer at the dinner table and a boss who was allegedly applying for a security clearance. That is a small business with very good connections.
New name, same crew
The sanctions created a real business problem for them. In October 2020 OFAC published an advisory warning that paying a ransom to a sanctioned group may violate US sanctions rules, and it named Evil Corp. From that day the brand was poison. Nobody wants to wire money to a group literally called Evil Corp.
So they did what any company with a reputation problem does: they rebranded. Per the NCA, after 2019 members of the group used WastedLocker (from mid-2020), then Hades, PhoenixLocker, PayloadBIN and Macaw. Between 2022 and 2024 members worked as affiliates of LockBit, the biggest ransomware program of those years. The NCA also says one PhoenixLocker attack brought in a $40 million payment, the largest recorded at the time.
Picture the pitch: "Hi, we are a brand new ransomware group, we have nothing to do with that sanctioned family, our code just happens to look similar, and the payment is in crypto, and if you don't pay we can't give your files back." Not sketchy at all.
In October 2024 the UK, the US and Australia sanctioned more of them, the UK alone named 16 members, and the DOJ unsealed an indictment against Ryzhenkov in the Northern District of Texas for BitPaymer ransomware attacks on victims in Texas and across the US.
Why nobody collects the $5 million
When I watch a ransomware program, I look for the unhappy people: an affiliate who got shorted, a coder who didn't get paid, someone who got banned from a forum. That is usually where the leaks come from. Conti is the textbook example, and I spent a lot of time in those leaks.
A family business is much harder. Nobody quits, and the person who would have the most to gain from talking is the father-in-law who used to work at the FSB. A $5 million bounty only works if someone close to you wants it.
As for Yakubets himself: in November 2026, the Russian outlet Meduza reported, based on documents it says it obtained, that he vacations at luxury resorts inside Russia and that in October 2025 he and his wife paid more than four million rubles at a resort in the Altai Mountains. The NCA has said that if he leaves Russia, he will be arrested and sent to the US. So he does not leave Russia, and Russia has a lot of nice mountains.
The circle doesn't break
Look at the timeline: Zeus in 2009, Dridex in 2014, BitPaymer, then WastedLocker, then four more names, then LockBit. Same people, new costume every year or two. This is exactly what I mean when I say the circle doesn't break. The technology changed three times and the family stayed the same.
My prediction: Yakubets stays home, the family keeps changing logos, and in 2029 someone writes the ten-year version of this post with the same wanted poster, unfortunately.
I hope I improved 0.1% of your knowledge. If you want to go look yourself, the FBI wanted poster and the 2024 NCA release are both public and worth ten minutes.
See you next time!
Sources
- US Department of Justice and FBI, charges against Maksim Yakubets and Igor Turashev, December 5, 2019, and the FBI wanted poster for Yakubets.
- US Treasury (OFAC), "Treasury Sanctions Evil Corp, the Russia-Based Cybercriminal Group Behind Dridex Malware", December 5, 2019.
- UK National Crime Agency, December 5, 2019 release on Evil Corp.
- US Treasury (OFAC), ransomware payments advisory, October 1, 2020.
- UK National Crime Agency, "Further members of Evil Corp cyber crime group exposed, one unmasked as LockBit affiliate", October 2024, and "Evil Corp: Behind the Screens".
- US Treasury, Evil Corp designations, October 1, 2024.
- US Attorney's Office, Northern District of Texas, Ryzhenkov indictment, October 1, 2024.
- Meduza, November 9, 2026, on sanctioned Russians at a luxury resort in the Altai Mountains.
All charges are allegations. Yakubets, Turashev and Ryzhenkov are presumed innocent until proven guilty in court.